

Breachsense Brings Its Dark Web Monitoring API to Claude Code, Codex and GitHub Copilot
News originally published by
EIN Presswire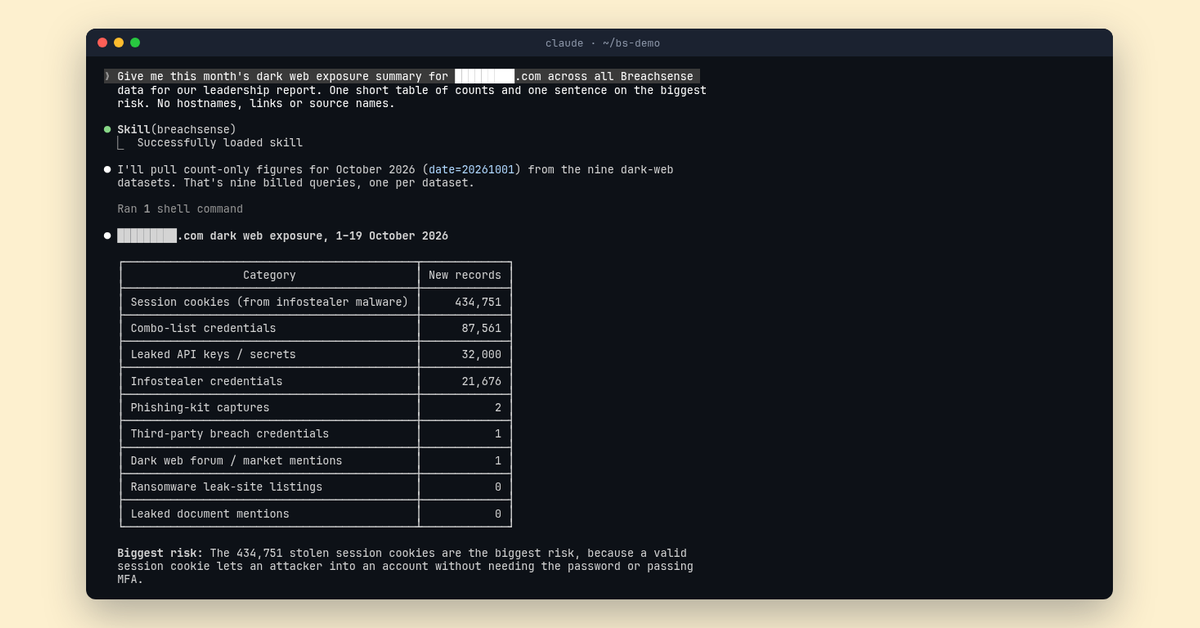
The Breachsense skill in Claude Code summarizes one company's new dark web records for October 2026, with the domain masked.
An open-source skill lets security teams ask about leaked credentials, session tokens, and company data from inside their LLM coding assistant.
A user types a question, such as whether anyone at their company's domain shows up in a new stealer log. The assistant chooses the right Breachsense endpoint and runs the query. It then summarizes the results. It also names the endpoint it called, so the user can verify the results.
With the skill:
• The assistant checks a domain or email address for stolen credentials. The sources include stealer logs, phishing kits, combo lists and third-party breaches.
• The assistant finds stolen session tokens and leaked API keys that stealer logs recorded for a company's domains.
• The assistant checks whether a vendor shows up on a ransomware leak site.
• The assistant searches the full text of files from ransomware leak sites, third-party breaches and unsecured databases. A company can use it to find its own contracts or internal documents in a vendor's breach.
The assistant can also add domains to a Breachsense watchlist and send its webhook alerts to a SIEM.
In Claude Code, users install the skill from the Breachsense GitHub repository with three commands. In Codex and GitHub Copilot, users copy the skill folder into their skills directory. Queries need a Breachsense license key.
"Security teams shouldn't need to babysit another vendor dashboard to find out what data leaked. The analysts who action our data already work in a terminal. More of them now keep a coding assistant open. When the SIEM flags a strange sign-in, they can check whether the employee's password was compromised. They can also look up the employee's other leaked passwords. MSSPs can look up leaked passwords for any client's employees," said Josh Amishav, Founder and CEO of Breachsense.
Install steps for Claude Code, Codex and GitHub Copilot see our LLM skill.
For details, security teams can book a demo.
About Breachsense
Breachsense is a dark web monitoring API for security teams and MSSPs. It tells them when their own data, or a vendor's, has already been stolen. It finds leaked credentials in stealer logs, combo lists, phishing kits and third-party breaches. It also finds stolen session tokens, leaked API keys and one-time MFA codes typed into phishing pages. Teams can search files leaked in ransomware attacks, third-party breaches and unsecured databases for their company's data. Breachsense sends
Breachsense
sales@breachsense.com
Josh Amishav
Visit us on social media:
LinkedIn
Legal Disclaimer:
EIN Presswire provides this news content "as is" without warranty of any kind. We do not accept any responsibility or liability for the accuracy, content, images, videos, licenses, completeness, legality, or reliability of the information contained in this article. If you have any complaints or copyright issues related to this article, kindly contact the author above.
